


 |
市場調查報告書
商品編碼
2123019
異常檢測:市場佔有率分析、產業趨勢與統計、成長預測(2026-2031)Anomaly Detection - Market Share Analysis, Industry Trends & Statistics, Growth Forecasts (2026 - 2031) |
||||||

※ 本網頁內容可能與最新版本有所差異。詳細情況請與我們聯繫。
根據 Mordor Intelligence 預測,異常檢測市場規模預計將在 2026 年達到 76.3 億美元,並在 2031 年擴大到 166.3 億美元,在整個預測期內保持 16.86% 的強勁複合年成長率。
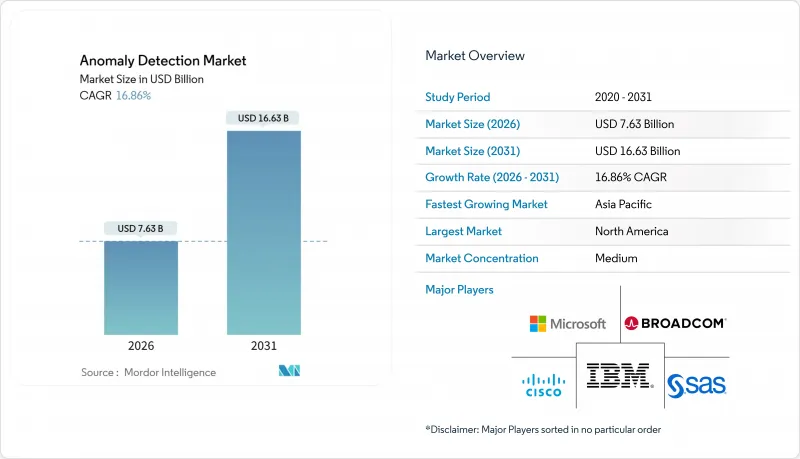
本報告按元件(解決方案和服務)、部署模式(本地部署、雲端部署、混合部署)、最終用戶產業(製造業、醫療產業等)、技術(巨量資料分析等)、組織規模(中小企業和大型企業)、應用程式(詐欺偵測、入侵偵測等)和地區進行細分。市場預測以美元計價。
全球異常檢測市場趨勢與洞察
針對關鍵基礎設施的網路攻擊日益增多
2024年和2025年,網路攻擊者將攻擊目標從IT轉向營運技術(OT),利用工廠網路和企業系統的整合。美國能源局記錄顯示,2024年針對電力公司的攻擊事件達387起,比2023年增加了41%,其中68%的攻擊涉及繞過基於特徵碼檢測工具的異常控制指令。隨後,美國運輸安全管理局(TSA)發布指令,強制管線營運商實施持續異常監控,加速了先前依賴空氣間隙防禦的產業採用該技術。更新後的IEC 62443指南將異常檢測定位為傳統控制器無法修補時的補償性控制手段,推動了設備生命週期超過20年的公共產業和製造業領域的新項目。
擴大異常檢測技術在銀行、金融服務和保險(BFSI)產業反詐騙的應用。
隨著即時結算機制和開放銀行API的普及,詐欺目標範圍不斷擴大,銀行正擴大採用行為分析技術來檢測設備、地理位置和交易速度的異常情況。 FedNow服務預計在2025年處理7,400萬筆交易,總額達450億美元,其不可逆性提高了金融機構的風險接受度。摩根大通在2025年投資21億美元用於反詐騙技術,並在實施異常檢測演算法後,報告誤報率降低了34%。修訂後的歐洲支付服務指示要求採用強客戶身份驗證和即時風險評分,進一步將異常檢測整合到核心銀行平台中。
強大的開放原始碼異常檢測庫的出現導致付費許可證的使用率下降。
像 PyOD 和 Alibi Detect 這樣的生產就緒型框架已經獲得了許多開發者的支持,其中 PyOD 截至 2025 年 12 月在 GitHub 上的星標數已超過 8200。預算有限的中小型企業也擴大選擇這些工具,尤其是在效能監控和預測性維護領域。雖然開放原始碼缺乏企業級支援和合規性認證,但社群貢獻正在逐步趕上專有軟體的功能集,從而降低了低階市場的價格。 Linux 基金會於 2024 年發布的對抗性穩健性工具箱進一步擴展了基準異常檢測的通用性,這將進一步降低授權收入。
細分市場分析
到2025年,解決方案將主導市場,佔據異常檢測市場66.71%的佔有率。這反映了網路行為和使用者行為分析在雲端和本地環境中的廣泛應用。然而,隨著企業尋求外部專家來最佳化演算法、將分析結果整合到安全編配和回應手冊中,以及解決模型漂移問題,預計到2031年,業務收益將以17.11%的複合年成長率成長。專業服務已成為平台供應商的策略收入來源。 Splunk在2025年實現了22%的年成長。對於缺乏安全營運中心(SOC)的中小型企業而言,託管服務極具吸引力,它以訂閱模式提供全天候監控。
對維運支援的需求源自於模型日益成長的複雜性。基於變壓器的偵測器需要針對特定領域進行特徵工程、超參數調優,並定期重新訓練以適應不斷變化的流量模式。企業擴大將持續諮詢服務協議與初始軟體購買捆綁在一起,從而提升了服務在總合約價值(TCV)中的重要性。這一趨勢有利於能夠提供認證人員和基於績效的服務等級協定(SLA)的供應商,使客戶能夠專注於核心業務,而供應商則能確保持續的收入。
到2025年,雲端部署將佔據異常偵測市場58.91%的佔有率,這主要得益於雲端強大的運算能力,能夠進行Petabyte級模型訓練。然而,混合架構正以17.39%的複合年成長率迅速成長,成為受監管產業(必須將敏感遙測資料保留在本地)的標準選擇。歐盟的《數位營運彈性法案》要求金融機構即使在雲端供應商故障的情況下也能確保業務連續性,這推動了在本地設備上運行推理引擎並將聚合特徵發送到雲端進行模型開發的趨勢。
這種模式利用雲端規模學習最佳化了延遲和成本,同時無需將原始資料傳送到外部。擁有高頻感測器快取的製造商將運行資料保留在工廠內部,在區域雲區訓練模型,然後將壓縮後的權重推送回邊緣閘道器。這種工作流程使企業能夠在遵守印度、德國和加拿大資料主權法規的同時,繼續存取僅在公共雲端上提供的高階人工智慧框架。
區域分析
到2025年,北美將佔據異常檢測市場39.83%的佔有率。這主要得益於嚴格的資料外洩通知法律和成熟的威脅情報網。根據美國行政管理和預算辦公室(OMB)第22-09號備忘錄,美國聯邦機構將被要求在2026財政年度之前實施行為分析。加拿大修訂後的《隱私法》對金融服務和醫療保健提供者施加了類似的義務,進一步擴大了國內需求。
亞太地區是成長最快的地區,年複合成長率達17.82%。中國將於2024年修訂《網路安全法》,強制要求關鍵資訊基礎設施營運商實施異常檢測系統;印度的《數位個人資料保護法》則強制要求對跨境資料傳輸進行行為監控。日本經濟產業省發布了《互聯產業指南》,建議在汽車和電子工廠中使用異常檢測技術。韓國個人資料保護機構將於2025年對監控系統不完善的企業處以610萬美元的罰款,這正在推動電信和電子商務行業更廣泛地採用異常檢測技術。
在歐洲,人們正在努力平衡強力的隱私保護和日益成長的網路彈性需求。 NIS2 要求關鍵服務提供者建立持續監控系統,但 GDPR 的資料最小化原則限制了對詳細行為日誌的訪問,從而促進了本地部署和聯邦學習模型的發展。德國 BSI 指南將異常檢測視為傳統工業控制器的一種補償性控制措施,這推動了其在化學和汽車行業叢集中的應用。英國國家網路安全中心 (NCSC) 的報告顯示,到 2025 年,68% 的大型企業將實施異常檢測,高於 2024 年的 54%。
中東、非洲和南美洲正成為與國家網路安全戰略相關的新興需求中心。在阿拉伯聯合大公國(阿拉伯聯合大公國)和沙烏地阿拉伯,關鍵基礎設施的持續監控已成為強制性要求,這加速了能源和交通運輸領域的相關項目。巴西資料保護機構於2024年發布指導意見,建議採用行為分析技術來檢測未授權存取,這加快了該技術在銀行業和醫療保健領域的應用。
其他好處:
- Excel格式的市場預測(ME)表
- 三個月的分析師支持
目錄
第1章:引言
- 研究假設和市場定義
- 調查範圍
第2章:調查方法
第3章執行摘要
第4章 市場狀況
- 市場概覽
- 市場促進因素
- 針對關鍵基礎設施的網路攻擊日益增多
- 擴大異常檢測技術在銀行、金融服務和保險(BFSI)行業詐欺預防的應用。
- 物聯網設備的激增正在擴大攻擊面。
- 透過AIOps和異常檢測的整合實現自主事件回應。
- 邊緣人工智慧晶片的興起,使得設備內即時異常分析成為可能。
- 政府已將強制性行為監控納入其零信任安全框架。
- 市場限制因素
- 功能強大的開放原始碼異常檢測庫的出現,導致付費許可證的使用率下降。
- 缺乏能夠調優模型的熟練資料科學家。
- 動態資料環境下的模型漂移正在增加維護成本。
- 隱私法規限制對用於行為分析的高粒度資料的存取。
- 產業價值鏈分析
- 監理情勢
- 技術展望
- 波特五力分析
- 宏觀經濟因素對市場的影響
第5章 市場規模與成長預測
- 按組件
- 解決方案
- 網路運作中的異常檢測
- 異常使用者行為檢測
- 服務
- 專業服務
- 託管服務
- 解決方案
- 不同的發展
- 現場
- 雲
- 混合
- 按最終用戶行業分類
- 銀行、金融服務和保險(BFSI)
- 製造業
- 衛生保健
- 資訊科技/通訊
- 政府/國防
- 零售與電子商務
- 透過技術
- 機器學習和人工智慧
- 巨量資料分析
- 資料探勘和商業智慧
- 統計方法
- 按組織規模
- 小型企業
- 大公司
- 透過使用
- 詐欺偵測
- 入侵偵測
- 故障偵測與監控
- 資料外洩檢測
- 其他用途
- 按地區
- 北美洲
- 美國
- 加拿大
- 墨西哥
- 歐洲
- 德國
- 英國
- 法國
- 俄羅斯
- 其他歐洲國家
- 亞太地區
- 中國
- 日本
- 印度
- 韓國
- 澳洲
- 其他亞太國家
- 中東和非洲
- 中東
- 沙烏地阿拉伯
- 阿拉伯聯合大公國
- 其他中東國家
- 非洲
- 南非
- 埃及
- 其他非洲國家
- 中東
- 南美洲
- 巴西
- 阿根廷
- 其他南美國家
- 北美洲
第6章 競爭情勢
- 市場集中度
- 策略趨勢
- 市佔率分析
- 公司簡介
- IBM Corporation
- Cisco Systems Inc.
- Microsoft Corporation
- Splunk Inc.
- Broadcom Inc.
- SAS Institute Inc.
- Trend Micro Incorporated
- Wipro Limited
- Verint Systems Inc.
- Guardian Analytics Inc.
- Securonix Inc.
- Gurucul Solutions, LLC
- Anodot Ltd.
- Happiest Minds Technologies Pvt. Ltd.
- Hewlett Packard Enterprise Company
- Dell Technologies Inc.
- Google LLC
- Amazon Web Services Inc.
- Rapid7 Inc.
- Micro Focus International plc
- LogRhythm Inc.
第7章 市場機會與未來展望
According to Mordor Intelligence, the anomaly detection market size reached USD 7.63 billion in 2026 and is projected to rise to USD 16.63 billion by 2031, translating into a robust 16.86% CAGR over the forecast period.
This report is Segmented by Component (Solutions, and Services), Deployment (On-Premise, Cloud, Hybrid), End-User Industry (Manufacturing, Healthcare, and More), Technology (Big Data Analytics, and More), Organization Size (Small and Medium Enterprises, and Large Enterprises), Application (Fraud Detection, Intrusion Detection, and More), and Geography. Market Forecasts are Provided in Terms of Value (USD).
Global Anomaly Detection Market Trends and Insights
Increasing Number of Cyberattacks Targeting Critical Infrastructure
Cyber adversaries shifted from IT to operational technology in 2024 and 2025, exploiting the convergence of plant-floor networks with enterprise systems. The U.S. Department of Energy logged 387 incidents against electric utilities in 2024, 41% higher than 2023, and 68% involved anomalous control commands that bypassed signature-based tools. Subsequent directives from the Transportation Security Administration require pipeline operators to deploy continuous anomaly monitoring, accelerating uptake in sectors historically reliant on air-gapped defenses. Updated IEC 62443 guidance positions anomaly detection as a compensating control when patching legacy controllers is infeasible, driving new projects in utilities and manufacturing where equipment lifecycles exceed 20 years.
Growing Adoption of Anomaly Detection in Fraud Prevention Across BFSI
Instant payment schemes and open banking APIs widened the fraud surface, prompting banks to embrace behavioral analytics that flag deviations in device, geolocation, and transaction velocity. The FedNow service processed 74 million transactions worth USD 45 billion in 2025, and its irreversibility heightened institutions' risk tolerance. JPMorgan Chase spent USD 2.1 billion on fraud-prevention technology in 2025, reporting a 34% drop in false positives after deploying anomaly-detection algorithms. Europe's revised Payment Services Directive compels strong customer authentication with real-time risk scoring, further embedding anomaly detection in core banking platforms.
Availability of Robust Open-Source Anomaly Detection Libraries Reducing Paid License Uptake
Production-ready frameworks such as PyOD and Alibi Detect amassed a broad developer following, with PyOD surpassing 8,200 GitHub stars by December 2025. Small firms with lean budgets increasingly opt for these tools, especially for performance monitoring and predictive maintenance. Although open-source lacks enterprise support and compliance certifications, community contributions keep pace with proprietary feature sets, compressing vendor pricing at the lower end of the market. The Linux Foundation's Adversarial Robustness Toolbox, launched in 2024, further commoditizes baseline anomaly detection and exerts downward pressure on license revenues.
Other drivers and restraints analyzed in the detailed report include:
- Proliferation of IoT Devices Expanding Attack Surface
- Convergence of AIOps with Anomaly Detection to Enable Autonomous Incident Response
- Shortage of Skilled Data Scientists Capable of Tuning Models
For complete list of drivers and restraints, kindly check the Table Of Contents.
Segment Analysis
Solutions dominated the anomaly detection market with a 66.71% share in 2025, reflecting widespread deployment of network behavior analytics and user behavior analytics across cloud and on-premises environments. However, services revenue is rising at a 17.11% CAGR through 2031 as organizations seek external expertise to fine-tune algorithms, integrate outputs into security orchestration and response playbooks, and combat model drift. Professional services became a strategic revenue stream for platform vendors; Splunk recorded 22% year-over-year growth in its services line during 2025. Managed services appeal to small and medium enterprises lacking security operations centers, offering 24/7 monitoring on a subscription basis.
Demand for operational support stems from rising model complexity. Transformer-based detectors require domain-specific feature engineering, hyperparameter tuning, and periodic retraining to handle evolving traffic patterns. Enterprises increasingly bundle ongoing advisory contracts with initial software purchases, elevating the importance of services in total contract value. The trend favors vendors able to provide certified personnel and outcome-based service-level agreements, thereby locking in recurring revenue while customers focus on core business priorities.
Cloud deployments held 58.91% of the anomaly detection market share in 2025 because elastic compute enables petabyte-scale model training. Yet hybrid architectures, expanding at a 17.39% CAGR, are emerging as the default among regulated industries that must retain sensitive telemetry on-premises. The European Union's Digital Operational Resilience Act obliges financial firms to ensure continuity even if a cloud vendor fails, prompting rollouts in which inference engines run on local appliances and aggregated features are sent to the cloud for model development.
This pattern optimizes latency and cost by eliminating raw-data egress while exploiting cloud-scale learning. Manufacturers with high-frequency sensor caches keep operational data in factories, train models in regional cloud zones, and then push compressed weights back to edge gateways. Such workflows help organizations comply with data-sovereignty statutes in India, Germany, and Canada, while maintaining access to advanced AI frameworks available only in public clouds.
Complete Report Scope:
- By Component
- Solutions
- Network Behavior Anomaly Detection
- User Behavior Anomaly Detection
- Services
- Professional Services
- Managed Services
- Solutions
- By Deployment
- On-Premise
- Cloud
- Hybrid
- By End-user Industry
- Banking, Financial Services and Insurance (BFSI)
- Manufacturing
- Healthcare
- IT and Telecommunications
- Government and Defense
- Retail and Ecommerce
- By Technology
- Machine Learning and Artificial Intelligence
- Big Data Analytics
- Data Mining and Business Intelligence
- Statistical Methods
- By Organization Size
- Small and Medium Enterprises
- Large Enterprises
- By Application
- Fraud Detection
- Intrusion Detection
- Fault Detection and Monitoring
- Data Exfiltration Detection
- Other Applications
- By Geography
- North America
- United States
- Canada
- Mexico
- Europe
- Germany
- United Kingdom
- France
- Russia
- Rest of Europe
- Asia-Pacific
- China
- Japan
- India
- South Korea
- Australia
- Rest of Asia-Pacific
- Middle East and Africa
- Middle East
- Saudi Arabia
- United Arab Emirates
- Rest of Middle East
- Africa
- South Africa
- Egypt
- Rest of Africa
- Middle East
- South America
- Brazil
- Argentina
- Rest of South America
- North America
Geography Analysis
North America accounted for 39.83% of the anomaly detection market share in 2025, driven by stringent breach-notification laws and mature threat intelligence networks. U.S. federal agencies must deploy behavioral analytics in accordance with OMB Memorandum 22-09 by fiscal 2026. Canada's amended privacy act imposes similar obligations on financial services and healthcare providers, expanding domestic demand.
Asia-Pacific is the fastest-growing region at a 17.82% CAGR. China's 2024 cybersecurity law amendments require critical information infrastructure operators to install anomaly detection systems, while India's Digital Personal Data Protection Act mandates behavioral monitoring for cross-border transfers. Japan's Ministry of Economy, Trade, and Industry issued connected-industry guidelines recommending the use of anomaly detection in automotive and electronics plants. South Korea's privacy regulator levied USD 6.1 million in fines during 2025 for inadequate monitoring, prompting broader adoption in telecommunications and e-commerce.
Europe balances strong privacy protections with growing cyber-resilience mandates. NIS2 requires essential-service operators to build continuous monitoring, yet GDPR's data-minimization principle restricts access to granular behavioral logs, spurring the development of on-premises and federated learning models. Germany's BSI guidelines recognize anomaly detection as a compensating control for legacy industrial controllers, thereby boosting adoption in chemical and automotive clusters. The U.K. National Cyber Security Centre reported 68% of large firms had deployed anomaly detection by 2025, up from 54% in 2024.
The Middle East and Africa, along with South America, represent emerging pockets of demand tied to national cybersecurity strategies. The United Arab Emirates and Saudi Arabia mandate continuous monitoring for critical infrastructure, accelerating projects in energy and transportation. Brazil's data-protection authority published guidance in 2024 that endorses behavioral analytics for unauthorized-access detection, catalyzing deployments in banking and healthcare.
- IBM Corporation
- Cisco Systems Inc.
- Microsoft Corporation
- Splunk Inc.
- Broadcom Inc.
- SAS Institute Inc.
- Trend Micro Incorporated
- Wipro Limited
- Verint Systems Inc.
- Guardian Analytics Inc.
- Securonix Inc.
- Gurucul Solutions, LLC
- Anodot Ltd.
- Happiest Minds Technologies Pvt. Ltd.
- Hewlett Packard Enterprise Company
- Dell Technologies Inc.
- Google LLC
- Amazon Web Services Inc.
- Rapid7 Inc.
- Micro Focus International plc
- LogRhythm Inc.
Additional Benefits:
- The market estimate (ME) sheet in Excel format
- 3 months of analyst support
TABLE OF CONTENTS
1 INTRODUCTION
- 1.1 Study Assumptions and Market Definition
- 1.2 Scope of the Study
2 RESEARCH METHODOLOGY
3 EXECUTIVE SUMMARY
4 MARKET LANDSCAPE
- 4.1 Market Overview
- 4.2 Market Drivers
- 4.2.1 Increasing Number of Cyberattacks Targeting Critical Infrastructure
- 4.2.2 Growing Adoption of Anomaly Detection in Fraud Prevention Across BFSI
- 4.2.3 Proliferation of IoT Devices Expanding Attack Surface
- 4.2.4 Convergence of AIOps with Anomaly Detection to Enable Autonomous Incident Response
- 4.2.5 Rise of Edge AI Chips Enabling Real-Time On-Device Anomaly Analytics
- 4.2.6 Mandatory Behavioral Monitoring in Zero Trust Security Frameworks Rolled Out by Governments
- 4.3 Market Restraints
- 4.3.1 Availability of Robust Open-Source Anomaly Detection Libraries Reducing Paid License Uptake
- 4.3.2 Shortage of Skilled Data Scientists Capable of Tuning Models
- 4.3.3 Model Drift in Dynamic Data Environments Increasing Maintenance Costs
- 4.3.4 Privacy Regulations Limiting Access to High-Granularity Data for Behavioral Analytics
- 4.4 Industry Value Chain Analysis
- 4.5 Regulatory Landscape
- 4.6 Technological Outlook
- 4.7 Porter's Five Forces Analysis
- 4.7.1 Bargaining Power of Suppliers
- 4.7.2 Bargaining Power of Buyers
- 4.7.3 Threat of New Entrants
- 4.7.4 Threat of Substitutes
- 4.7.5 Intensity of Competitive Rivalry
- 4.8 Impact of Macroeconomic Factors on the Market
5 MARKET SIZE AND GROWTH FORECASTS (VALUE)
- 5.1 By Component
- 5.1.1 Solutions
- 5.1.1.1 Network Behavior Anomaly Detection
- 5.1.1.2 User Behavior Anomaly Detection
- 5.1.2 Services
- 5.1.2.1 Professional Services
- 5.1.2.2 Managed Services
- 5.1.1 Solutions
- 5.2 By Deployment
- 5.2.1 On-Premise
- 5.2.2 Cloud
- 5.2.3 Hybrid
- 5.3 By End-user Industry
- 5.3.1 Banking, Financial Services and Insurance (BFSI)
- 5.3.2 Manufacturing
- 5.3.3 Healthcare
- 5.3.4 IT and Telecommunications
- 5.3.5 Government and Defense
- 5.3.6 Retail and Ecommerce
- 5.4 By Technology
- 5.4.1 Machine Learning and Artificial Intelligence
- 5.4.2 Big Data Analytics
- 5.4.3 Data Mining and Business Intelligence
- 5.4.4 Statistical Methods
- 5.5 By Organization Size
- 5.5.1 Small and Medium Enterprises
- 5.5.2 Large Enterprises
- 5.6 By Application
- 5.6.1 Fraud Detection
- 5.6.2 Intrusion Detection
- 5.6.3 Fault Detection and Monitoring
- 5.6.4 Data Exfiltration Detection
- 5.6.5 Other Applications
- 5.7 By Geography
- 5.7.1 North America
- 5.7.1.1 United States
- 5.7.1.2 Canada
- 5.7.1.3 Mexico
- 5.7.2 Europe
- 5.7.2.1 Germany
- 5.7.2.2 United Kingdom
- 5.7.2.3 France
- 5.7.2.4 Russia
- 5.7.2.5 Rest of Europe
- 5.7.3 Asia-Pacific
- 5.7.3.1 China
- 5.7.3.2 Japan
- 5.7.3.3 India
- 5.7.3.4 South Korea
- 5.7.3.5 Australia
- 5.7.3.6 Rest of Asia-Pacific
- 5.7.4 Middle East and Africa
- 5.7.4.1 Middle East
- 5.7.4.1.1 Saudi Arabia
- 5.7.4.1.2 United Arab Emirates
- 5.7.4.1.3 Rest of Middle East
- 5.7.4.2 Africa
- 5.7.4.2.1 South Africa
- 5.7.4.2.2 Egypt
- 5.7.4.2.3 Rest of Africa
- 5.7.4.1 Middle East
- 5.7.5 South America
- 5.7.5.1 Brazil
- 5.7.5.2 Argentina
- 5.7.5.3 Rest of South America
- 5.7.1 North America
6 COMPETITIVE LANDSCAPE
- 6.1 Market Concentration
- 6.2 Strategic Moves
- 6.3 Market Share Analysis
- 6.4 Company Profiles (includes Global Level Overview, Market Level Overview, Core Segments, Financials as available, Strategic Information, Market Rank/Share for Key Companies, Products and Services, and Recent Developments)
- 6.4.1 IBM Corporation
- 6.4.2 Cisco Systems Inc.
- 6.4.3 Microsoft Corporation
- 6.4.4 Splunk Inc.
- 6.4.5 Broadcom Inc.
- 6.4.6 SAS Institute Inc.
- 6.4.7 Trend Micro Incorporated
- 6.4.8 Wipro Limited
- 6.4.9 Verint Systems Inc.
- 6.4.10 Guardian Analytics Inc.
- 6.4.11 Securonix Inc.
- 6.4.12 Gurucul Solutions, LLC
- 6.4.13 Anodot Ltd.
- 6.4.14 Happiest Minds Technologies Pvt. Ltd.
- 6.4.15 Hewlett Packard Enterprise Company
- 6.4.16 Dell Technologies Inc.
- 6.4.17 Google LLC
- 6.4.18 Amazon Web Services Inc.
- 6.4.19 Rapid7 Inc.
- 6.4.20 Micro Focus International plc
- 6.4.21 LogRhythm Inc.
7 MARKET OPPORTUNITIES AND FUTURE OUTLOOK
- 7.1 White-space and Unmet-Need Assessment

 異常檢測市場-2026-2032年全球市場預測
 2026年全球獸醫訊號檢測與分析市場報告
 詐欺偵測與風險分析市場預測-全球詐欺類型、偵測方法、風險等級、應用、最終用戶與地區分析-2034年2026年全球網路安全分析市場報告2026年全球語音內容安全市場報告2026年全球價格異常檢測人工智慧市場報告2026年全球異常檢測市場報告2026年全球異常檢測解決方案市場報告
 異常檢測市場規模、佔有率和成長分析(按組件、技術、網路行為、用戶行為、部署類型、最終用途和地區分類)-產業預測,2026-2033年
 異常檢測,全球市場 2025-2029